The Expedia Breach Shows Why Companies Should Stop Hoarding Customer Data
Expedia Group's disclosure that attackers entered its systems through a third-party data provider is the latest reminder that businesses collect and keep far more personal information than they need, multiplying the damage when a single vendor is compromised.
On November 12, Expedia Group confirmed that intruders had reached its systems through a compromised third-party data platform. An extortion group has since claimed to hold hundreds of millions of traveler records, though investigators have not yet verified the scale or contents of any theft. The incident is still unfolding, but it has already revived a long-running debate in cybersecurity and privacy circles: why do companies keep so much information about their customers in the first place?
The problem is not just the breach
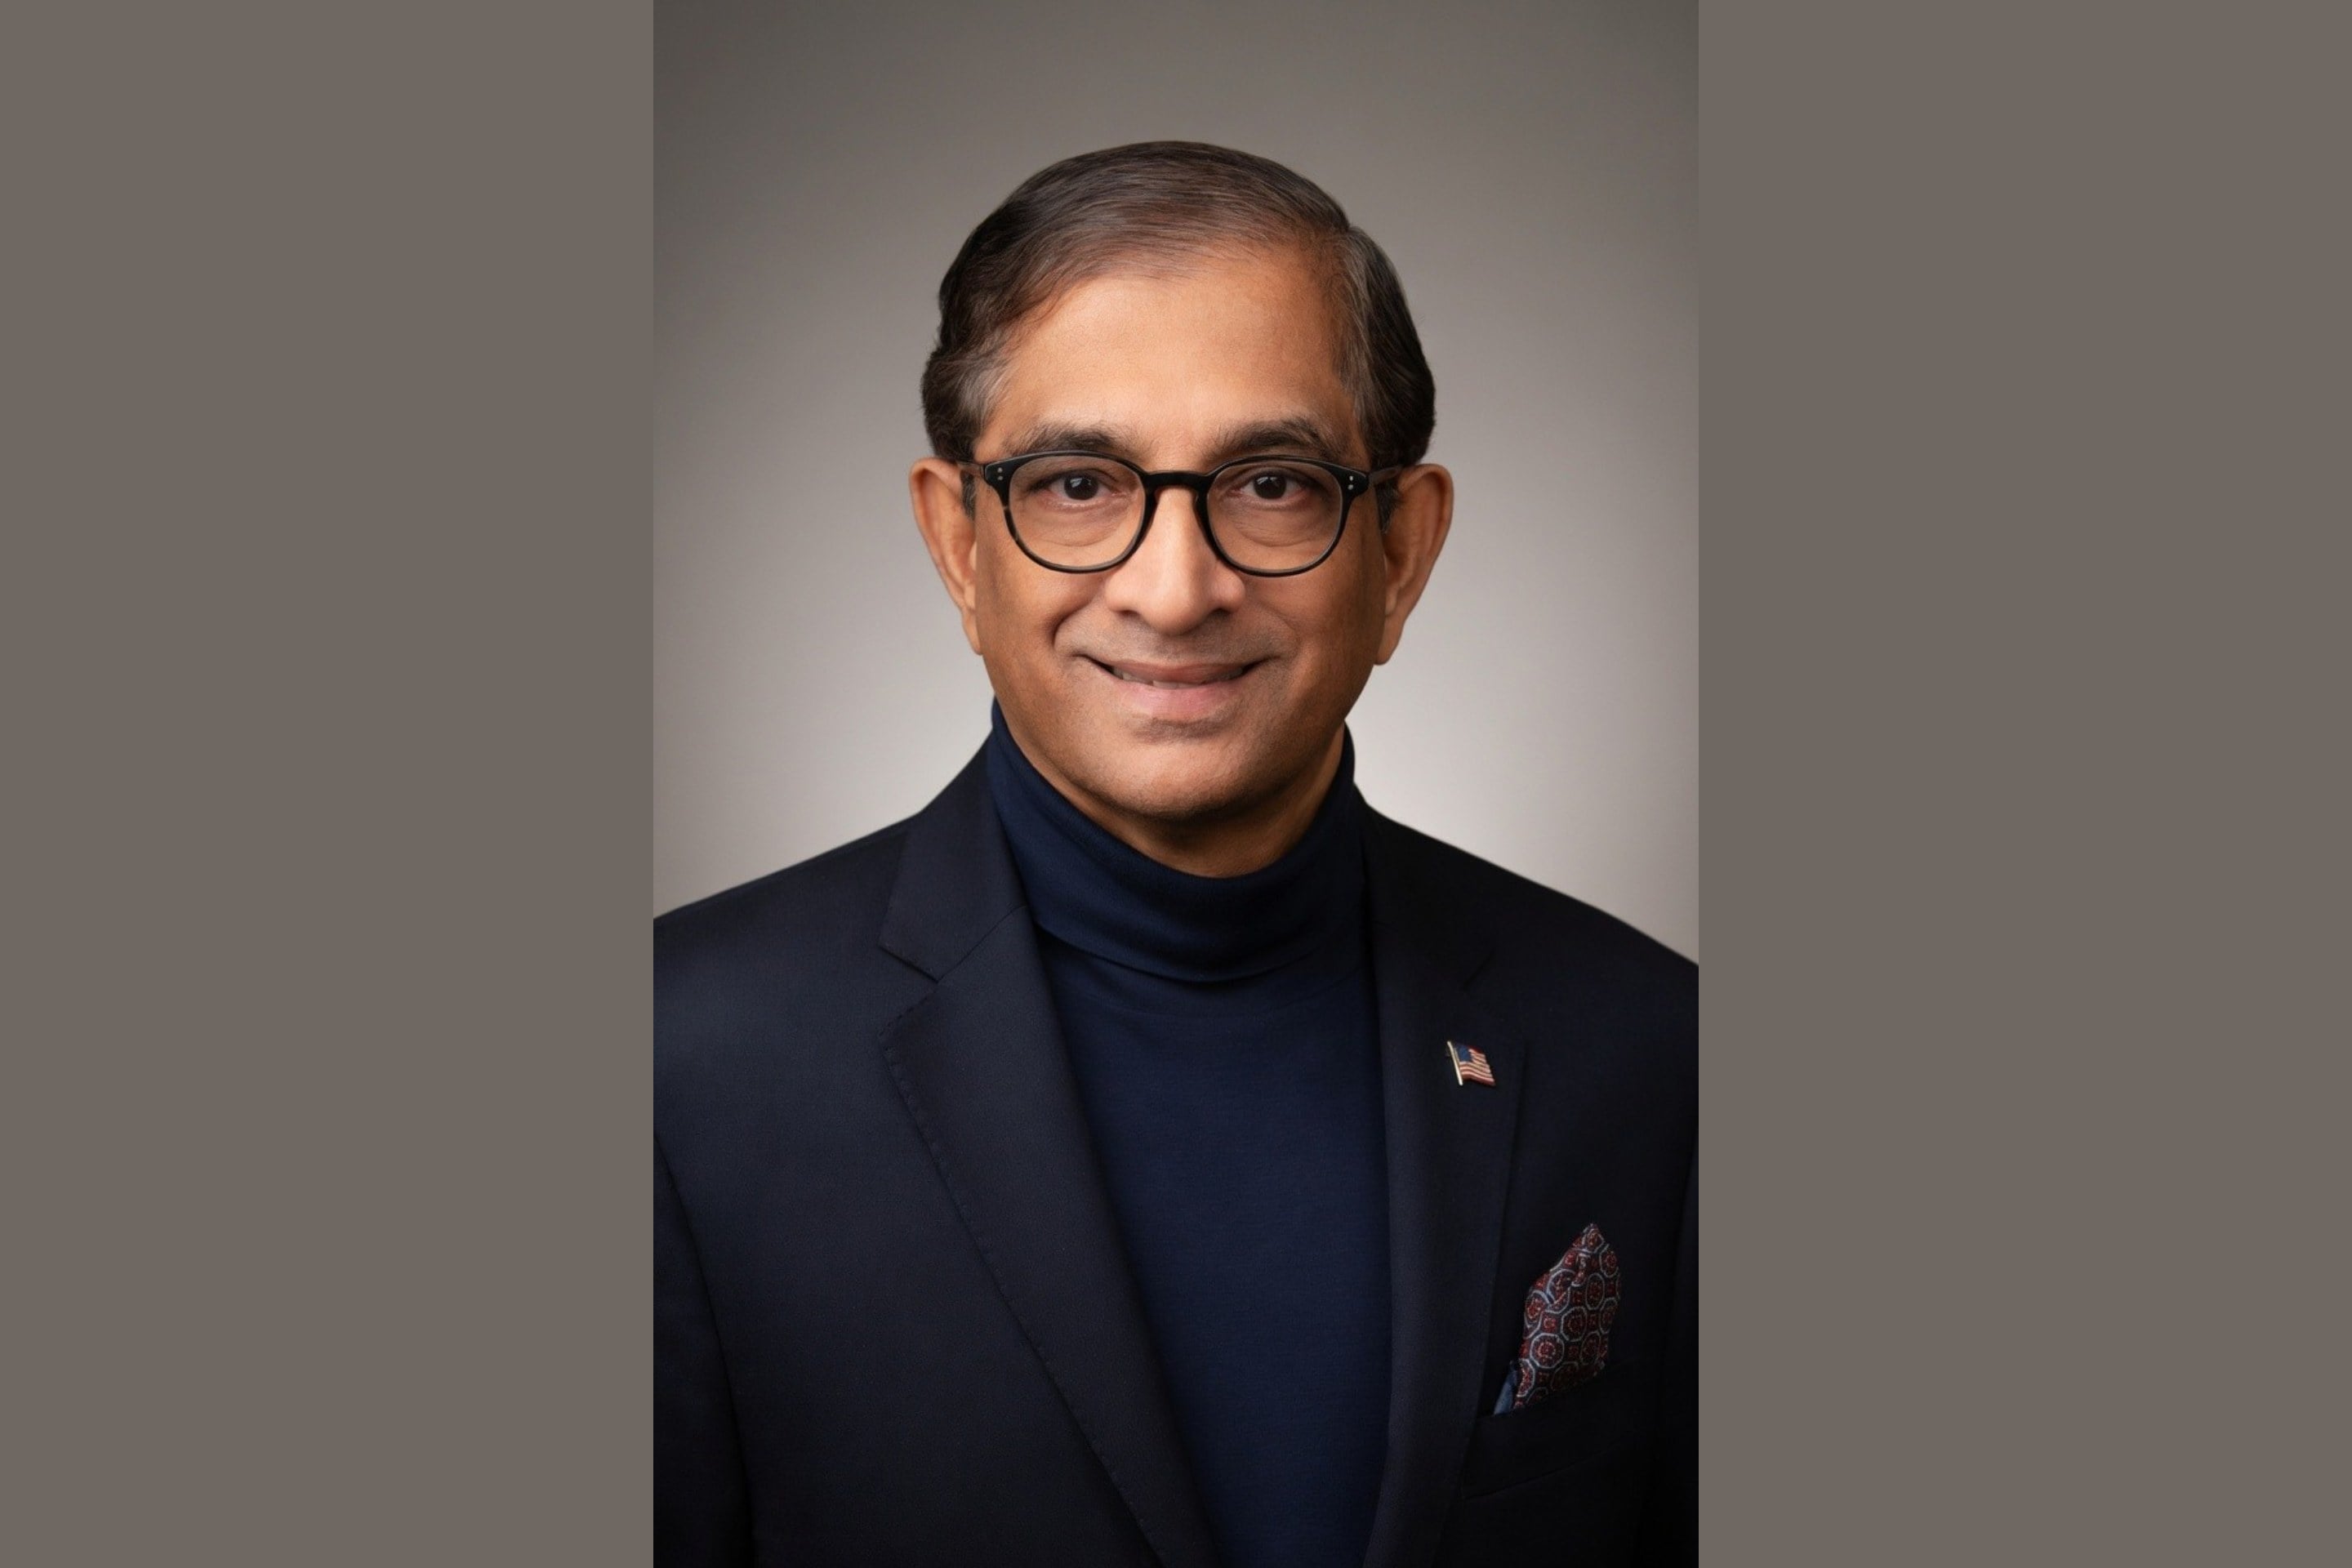
Raj Ananthanpillai, chief executive of identity verification firm Trua, argues that the real issue predates any single hack. In a commentary for Fortune, he wrote that businesses and their vendors routinely accumulate more personal data than a transaction requires and then store it indefinitely. When a trusted supplier is breached, the spillover can affect every company that shared records with it.
The Expedia case fits that pattern. The travel platform did not necessarily need to hold every detail it collected in order to book a room or a flight. Yet copies of identity documents, payment records, travel histories, and other information often migrate into vendor environments and remain there long after the original purchase.
A lesson from airport security
Ananthanpillai points to his earlier work on credentialing systems that eventually fed into TSA PreCheck and similar programs. The design question, he said, was not how much data the system could gather, but what the checkpoint actually needed to know.
Enrollment in such programs can involve government identification, background checks, and database queries. But at the screening lane, the only answer that matters is whether the traveler is approved. The officer does not need the full background file, Social Security number, or enrollment records. Those stay with the vetting authority, while the checkpoint relies on credential validation and biometric authentication. The result is a trustworthy determination without passing a dossier from system to system.
How overcollection grows quietly
Ananthanpillai cited one midsize staffing company that discovered roughly 180,000 applicant and worker records in its systems. About 35 percent were more than six years old, and more than half related to people who had never been hired or had left years earlier. Files containing Social Security numbers and background reports had been copied to at least four vendors and two client HR systems.
No single decision created that liability. It accumulated through onboarding forms, integrations, and the reflex to keep a record just in case. Most organizations, Ananthanpillai argues, do not need those permanent copies to make the decisions before them. A travel platform needs to confirm identity and payment validity. An employer needs to know whether an applicant holds a required credential. Those questions can be answered with limited, purpose-specific confirmations rather than full source documents.
Selective disclosure and the AI agent era
The alternative model is sometimes called selective disclosure. An individual undergoes strong verification once and then shares only the attribute or status required for a specific purpose. Mobile driver licenses and other attribute-verification systems already show how this can work in practice.
The approach does not eliminate cybersecurity risk, but it reduces the amount of sensitive information dispersed across corporate and vendor systems. Organizations that collect and retain less data shrink what an attacker can obtain, narrow the scope of third-party exposure, and make privacy obligations easier to manage. Insurers could treat unnecessary retention as a controllable risk, and individuals would face fewer consequences from breaches at companies they used only once.
The need for better identity models is becoming more urgent as AI agents begin taking actions on people's behalf. Organizations will need ways to establish who authorized a transaction and what the agent is permitted to do. Without a stronger model, that need could become an excuse to build even more identity databases.
From breach response to data diet
The full scope of the Expedia intrusion remains to be established. The broader lesson, Ananthanpillai wrote, is that as long as every business transaction generates another lasting store of personal records, a breach at one trusted provider will continue to create risks for many organizations and the people who rely on them.
The durable response, he argues, is not merely to defend ever-larger databases. It is to collect less, retain less, and share only what a particular decision requires. Businesses should treat unnecessary retention as a liability, insurers should price that liability, and policymakers should give data minimization as much attention as breach response. Otherwise, the headlines will keep repeating the same pattern.